How to Install Security Onion on Ubuntu: A Complete Guide
If you’ve been looking to boost your network’s visibility without splurging on pricey appliances, Security Onion is worth a glance. It bundles IDS, log management, and threat hunting tools into a single, Ubuntu‑friendly distro. Below you’ll find a step‑by‑step walkthrough that assumes a fresh Ubuntu 22.04 LTS install, but the concepts translate to other recent releases.
Why Choose Security Onion?
Security Onion isn’t just another packet sniffer; it’s a curated collection of open‑source sensors like Suricata, Zeek, and the Elastic Stack, all pre‑configured to talk to each other. This integration slashes the time you’d otherwise spend stitching together disparate components, letting you focus on interpreting alerts instead of wiring the plumbing.
Prerequisites and Planning
- At least 8 GB RAM – the Elastic Stack likes memory.
- 2 CPU cores (more if you expect heavy traffic).
- Static IP address or DHCP reservation for the host.
- Root or sudo privileges.
Make a note of the network interface you intend to monitor; you’ll need its name (e.g., eth0 or ens33) later.
Install Security Onion on Ubuntu: Preparing the System
First, bring the base system up to date. Running outdated libraries can cause dependency hiccups during the Security Onion installation.
sudo apt update && sudo apt upgrade -ysudo reboot
After the reboot, verify the kernel version. Security Onion prefers a recent kernel (5.15+ for Ubuntu 22.04); you can check with uname -r.
Step 1: Add the Security Onion Repository
Security Onion provides an official APT repository. Adding it is straightforward, but double‑check the URL in case the project has moved.
wget -qO - https://updates.securityonion.org/securityonion.asc | sudo apt-key add -echo "deb http://updates.securityonion.org/ubuntu focal main" | sudo tee /etc/apt/sources.list.d/securityonion.list
sudo apt update
If the key import throws a warning about “weak digest,” you can ignore it for now—Security Onion still validates packages before installation.
Step 2: Install the Core Packages
Run the meta‑package installer. It pulls in Suricata, Zeek, Elastic, Kibana, and a handful of utilities.
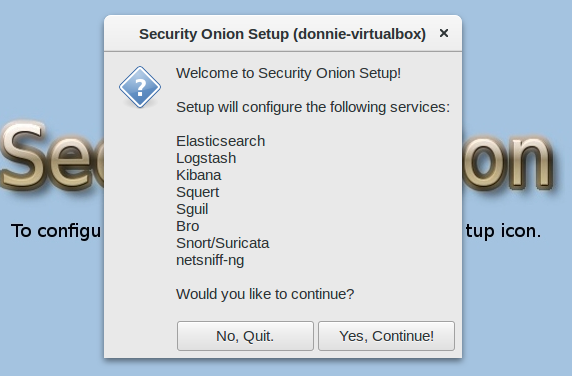
sudo apt install securityonion-all -yThe installer will ask a few configuration questions: whether this node will act as a sensor, server, or both; and which interface to sniff. Choose “All‑in‑One” if you’re testing on a single box.
Step 3: Run the Setup Wizard
Once the packages land, the real configuration begins. Launch the wizard with:
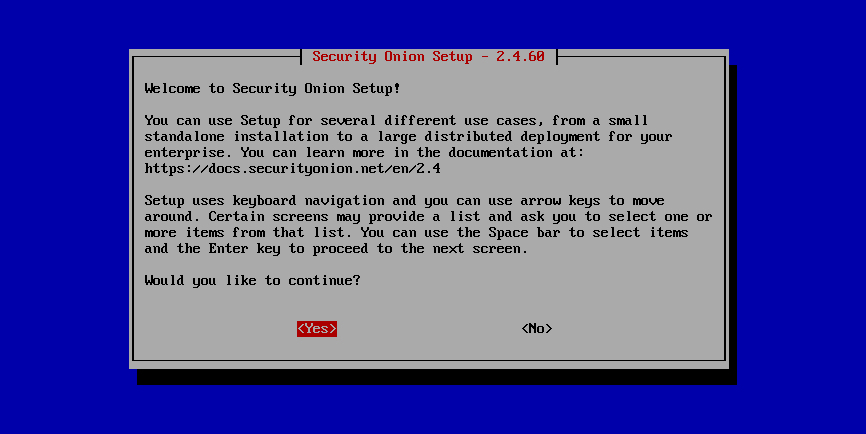
sudo so-setupThe wizard walks you through network settings, password creation for the Elastic user, and optional components like the Sguil UI. Pay attention to the “IP address for the Management Interface” – this is the address you’ll use to access the web UI later.
Step 4: Fine‑Tune Suricata and Zeek
Both sensors ship with default rule sets, but you’ll likely want to enable the Emerging Threats Open rules for broader coverage. Edit /etc/suricata/suricata.yaml and add the rule‑file path, then restart:
sudo systemctl restart suricatasudo systemctl restart zeek
Similarly, Zeek’s scripts live under /opt/zeek/share/zeek/site. Adding community scripts here can enrich DNS, SSL, and HTTP logs.
Step 5: Verify the Elastic Stack
Security Onion stores events in Elasticsearch and visualizes them via Kibana. After the setup wizard finishes, give the services a minute to start, then browse to https://your‑ip:5601. The first login uses the Elastic password you set earlier.
If Kibana shows a red “cluster health” warning, check the Elasticsearch logs (/var/log/elasticsearch) for memory‑related errors and consider increasing vm.max_map_count as the wizard suggests.
Step 6: Test the Sensors
A quick way to confirm everything is working is to generate some harmless traffic. Open a terminal on another machine and ping the Ubuntu host:
ping -c 5 your‑ubuntu‑ipBack in Kibana, navigate to “Discover” and filter by event_type:alert. You should see a Suricata ping alert, confirming the pipeline from sensor to UI.
Optional: Enable Automatic Updates
Security Onion’s rule sets evolve daily. To keep pace, enable the built‑in updater:
sudo so-rule-updateYou can schedule this via cron to run nightly, ensuring you never miss a critical signature.
Common Pitfalls and How to Avoid Them
- Insufficient RAM: Elastic can consume more than 4 GB under load. If you notice frequent “Out of memory” logs, add swap or upgrade RAM.
- Interface Mis‑selection: Sniffing the wrong NIC leads to empty logs. Double‑check
ip aoutput before the wizard. - Firewall Blocking: Ubuntu’s
ufwmay block ports 22, 443, and 5601. Open them withsudo ufw allow 22,443,5601/tcp.
Wrapping Up
With Security Onion up and running, you now have a powerful, open‑source NIDS/NIPS platform that can scale from a home lab to a modest enterprise. The initial effort of installation pays off in the rich context you gain from correlated logs, and the community around the project constantly contributes improvements.
Frequently Asked Questions
Can Security Onion run on a desktop Ubuntu install?
Yes, the all‑in‑one mode works on a typical desktop setup, though you’ll want to allocate enough RAM and disable power‑saving features that might throttle the network interface.
Do I need a dedicated NIC for monitoring?
It’s recommended but not mandatory. A separate NIC prevents the sensor from interfering with normal traffic on the host, especially when the host also serves as a gateway.
Is it safe to expose Kibana to the internet?
Generally no. Keep the web UI behind a VPN or restrict access with a firewall rule; exposing Kibana publicly can leak sensitive log data.
How often should I update the rule sets?
At least weekly. Security Onion’s so-rule-update script pulls the latest Emerging Threats rules, which often include critical fixes for newly discovered exploits.