How to Understand Archived Logs: First Time and Next Time
When you first stumble upon an archive of system logs, the sheer volume can feel overwhelming. Archived logs are essentially snapshots of past activity, compressed and stored for later reference. Whether you’re troubleshooting a recent outage or performing a routine audit, knowing how to read these records the first time—and how to reuse them later—can save hours of guesswork.
What Makes a Log Worth Archiving?
Not every log entry deserves a permanent home. Most organizations keep short‑term logs for real‑time monitoring, then move older entries to an archive to free up space and retain a historical trail. The criteria usually include:
- Critical security events that may need forensic analysis.
- Transaction records required for compliance regulations.
- Performance metrics useful for trend analysis over months or years.
By isolating these high‑value logs, you keep your active monitoring lean while preserving the data you’ll actually need later.
First‑Time Access: Getting Inside the Archive
The initial step is often the trickiest part: locating and opening the archived file. Most systems compress logs into formats like .gz, .zip, or proprietary containers. Here’s a quick checklist to get you started:
- Identify the storage location. Archives may live on a local disk, a network share, or a cloud bucket.
- Confirm the format. A
.gzfile, for instance, can be opened withgunzipor a GUI tool like 7‑Zip. - Choose a viewer. Plain‑text logs work with any editor, but large files benefit from specialized tools such as less, logrotate, or Splunk.
Once you’ve extracted a snippet, skim for timestamps and identifiers that match the incident you’re investigating. This quick scan often tells you whether the archive holds the clues you need.
Parsing the Data: From Raw Text to Actionable Insight
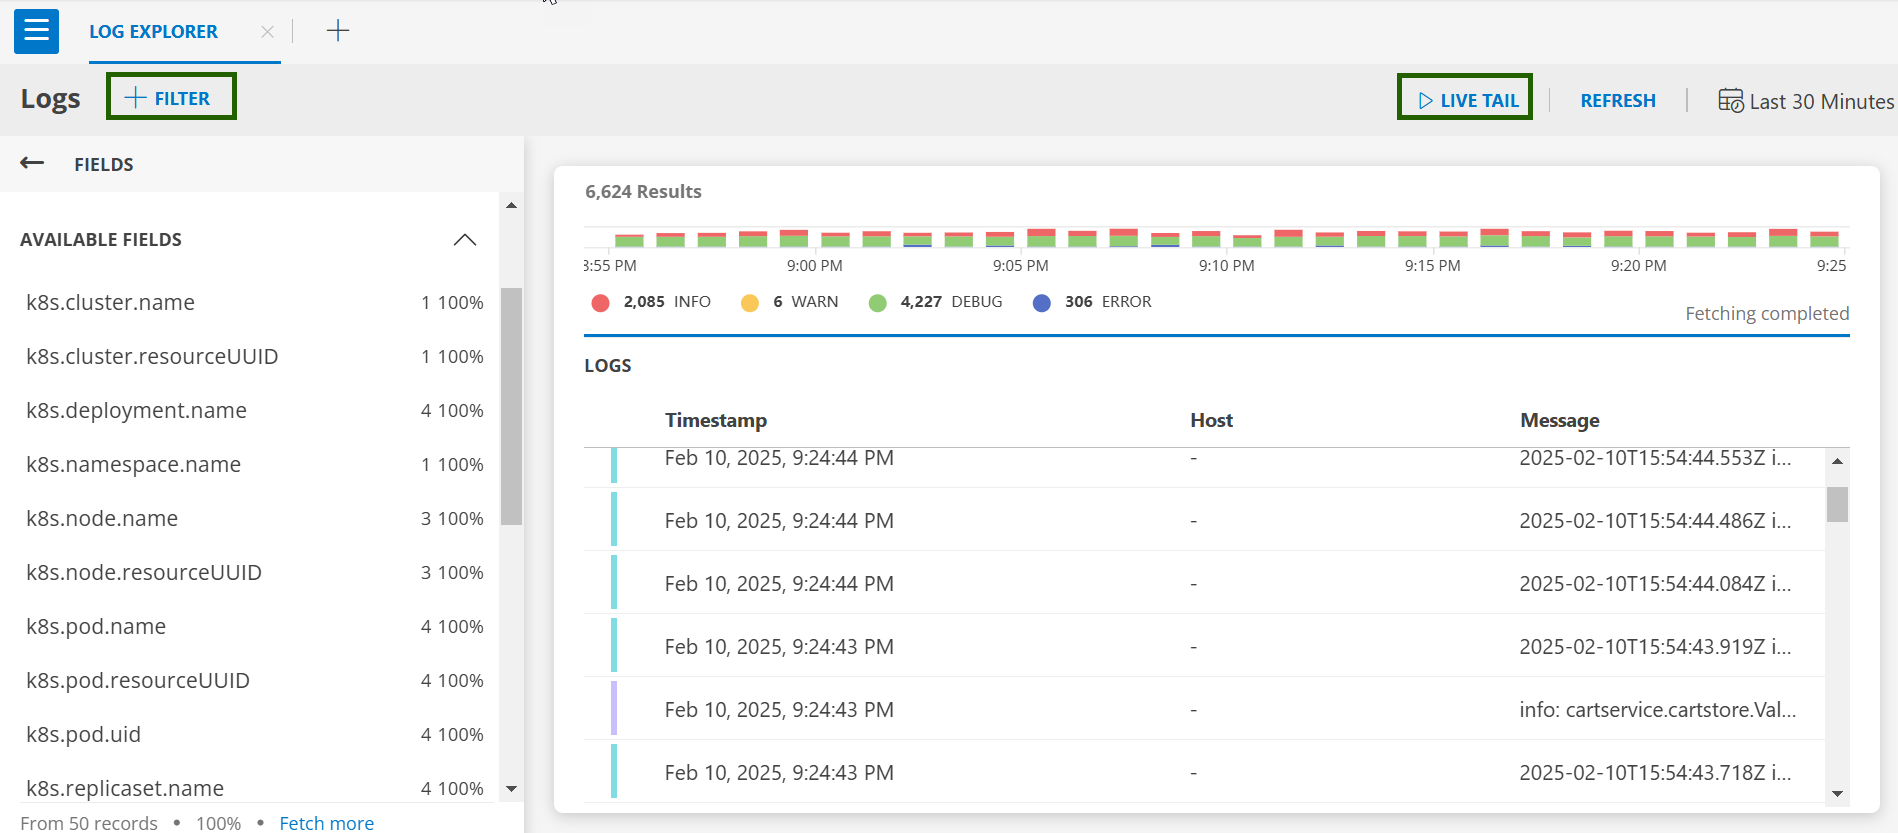
Archived logs are usually a sea of lines, each containing a timestamp, severity level, source, and message. The key is to filter out the noise. Common techniques include:
- Using
grepor PowerShell’sSelect-Stringto isolate keywords (e.g., “ERROR”, “AUTH_FAIL”). - Applying regular expressions to extract IP addresses or user IDs.
- Feeding the log into a log‑analysis platform that can automatically categorize events.
When you’ve narrowed the field, you can start piecing together a timeline. Look for patterns—repeated login failures, a spike in latency, or a cascade of service restarts—that point to root causes.
Re‑using Archived Logs: The “Next Time” Approach
The real power of an archive shows up when you turn historical data into proactive knowledge. Here are three ways to make archived logs work for you long after the initial review:
1. Build Baseline Metrics
By aggregating logs over weeks or months, you can establish what “normal” looks like for CPU usage, request rates, or error frequencies. Future alerts then trigger only when deviations exceed that baseline, reducing false positives.
2. Conduct Trend Analysis
Seasonal patterns often emerge—think higher traffic on Monday mornings or increased database locks during nightly batch jobs. Spotting these trends helps you schedule maintenance during low‑impact windows.
3. Support Compliance Audits
Many regulations require you to retain logs for a specific period and to produce them on demand. Having a well‑organized archive means you can quickly pull the exact records an auditor asks for, without scrambling through live files.
Best Practices for Maintaining an Archive
Even the most sophisticated analysis can’t compensate for a poorly managed archive. Keep these habits in mind:
- Rotate regularly. Set a retention policy—say, 90 days for security logs, 180 days for performance data—and automate the cleanup.
- Tag with metadata. Include source system, log type, and collection date in the filename or a side‑car JSON file. This makes searching later a breeze.
- Encrypt at rest. Logs often contain sensitive information; encrypting the archive protects against data breaches.
- Test restoration. Periodically verify that you can decompress and read a sample file; corrupted archives are a silent nightmare.
Common Pitfalls to Avoid
It’s easy to fall into habits that undermine the usefulness of archived logs. Watch out for:
- Over‑archiving: Storing everything indiscriminately creates storage bloat and makes genuine investigations slower.
- Neglecting timestamps: If clocks aren’t synchronized across systems, you’ll end up with a jumbled timeline that’s hard to reconcile.
- Relying on a single tool: Different log formats sometimes require different parsers; a one‑size‑fits‑all approach can miss critical entries.
Quick Reference Checklist
- Locate archive → Identify format → Decompress safely.
- Filter with keywords/regex → Build timeline → Diagnose issue.
- Extract metrics → Establish baselines → Set proactive alerts.
- Maintain rotation, metadata, encryption, and periodic tests.
FAQ
What exactly is an archived log?
An archived log is a stored copy of past log entries, typically compressed and kept for long‑term retention, compliance, or later analysis.
How can I search within a large archived log file?
Use command‑line utilities like grep, awk, or PowerShell’s Select-String, or import the file into a log‑management platform that supports indexed searching.
Do I need special permissions to access archived logs?
Usually yes—archived logs often contain sensitive data, so access is restricted to administrators or security personnel with appropriate clearance.
How long should I keep archived logs?
Retention periods depend on industry regulations and business needs; common practice ranges from 30 days for operational logs to several years for security or audit logs.