Mastering Grafana Alerting: A Step‑by‑Step Setup & Configuration Guide
Grafana’s alerting engine has become a cornerstone for teams that rely on real‑time insights. Whether you’re monitoring a Kubernetes cluster, tracking API latency, or simply keeping an eye on database health, a robust alerting system lets you catch anomalies before they snowball. This tutorial walks you through the Grafana alerting tutorial setup and configuration, covering everything from data source selection to notification channel management. By the time you finish, you’ll be able to define, test, and fine‑tune alerts that fit your organization’s exact needs.
Grafana Alerting Tutorial Setup & Configuration
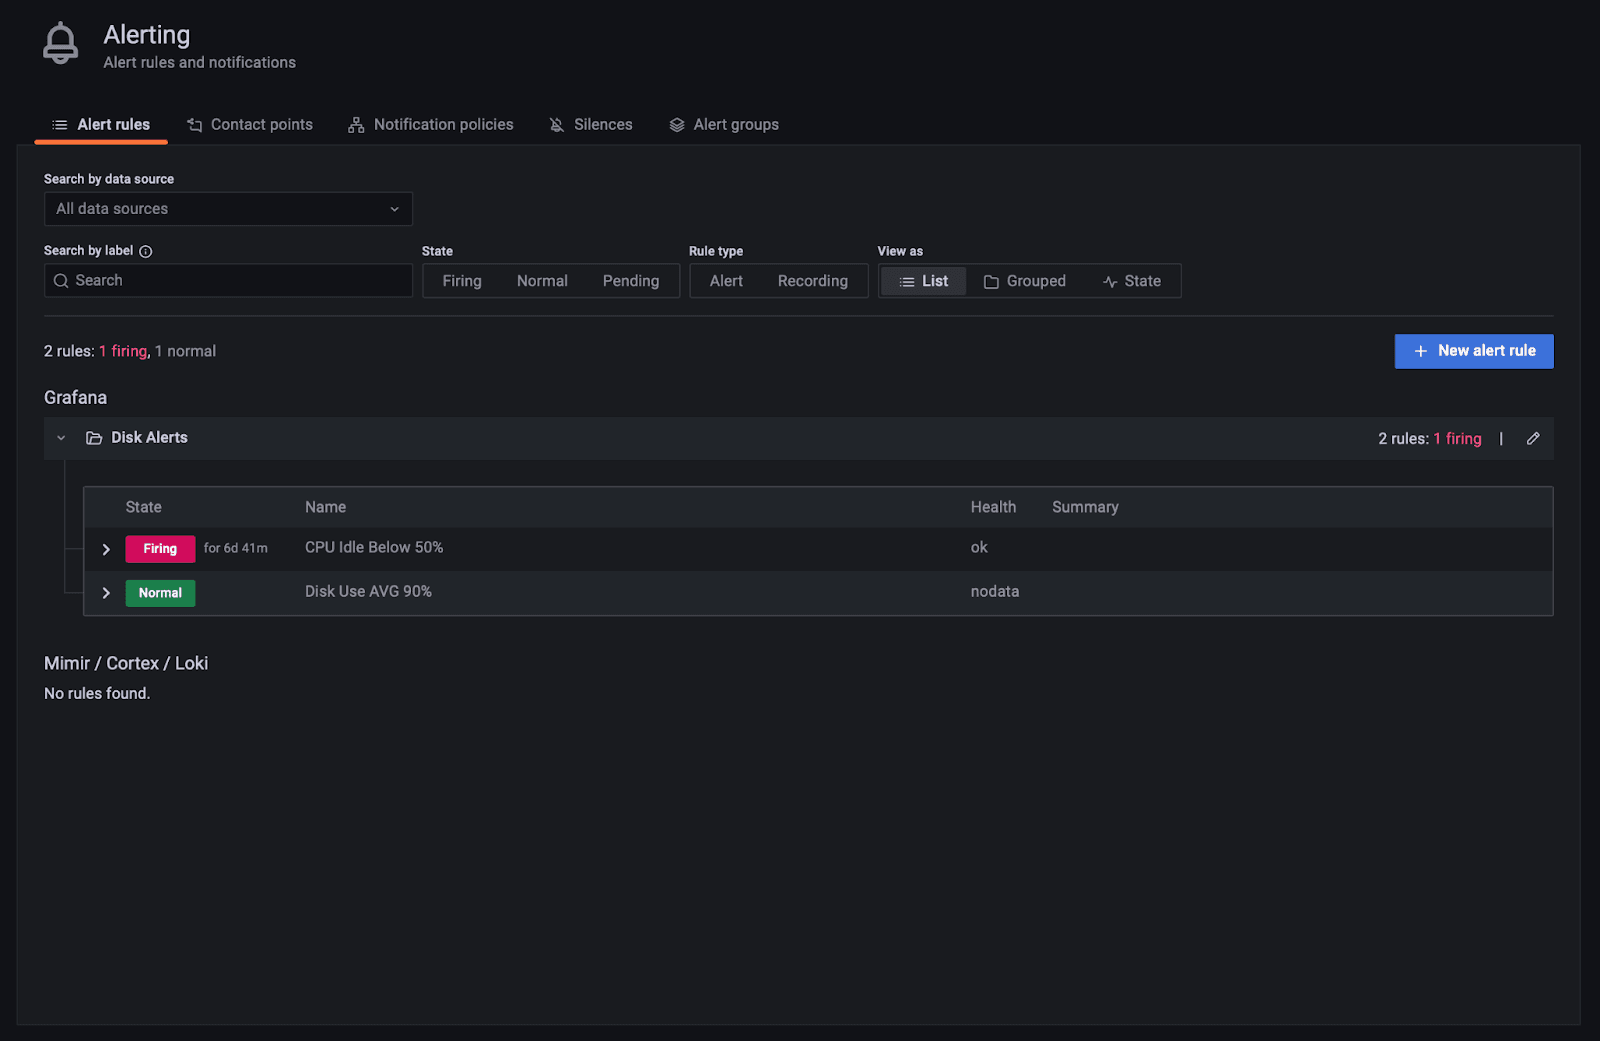
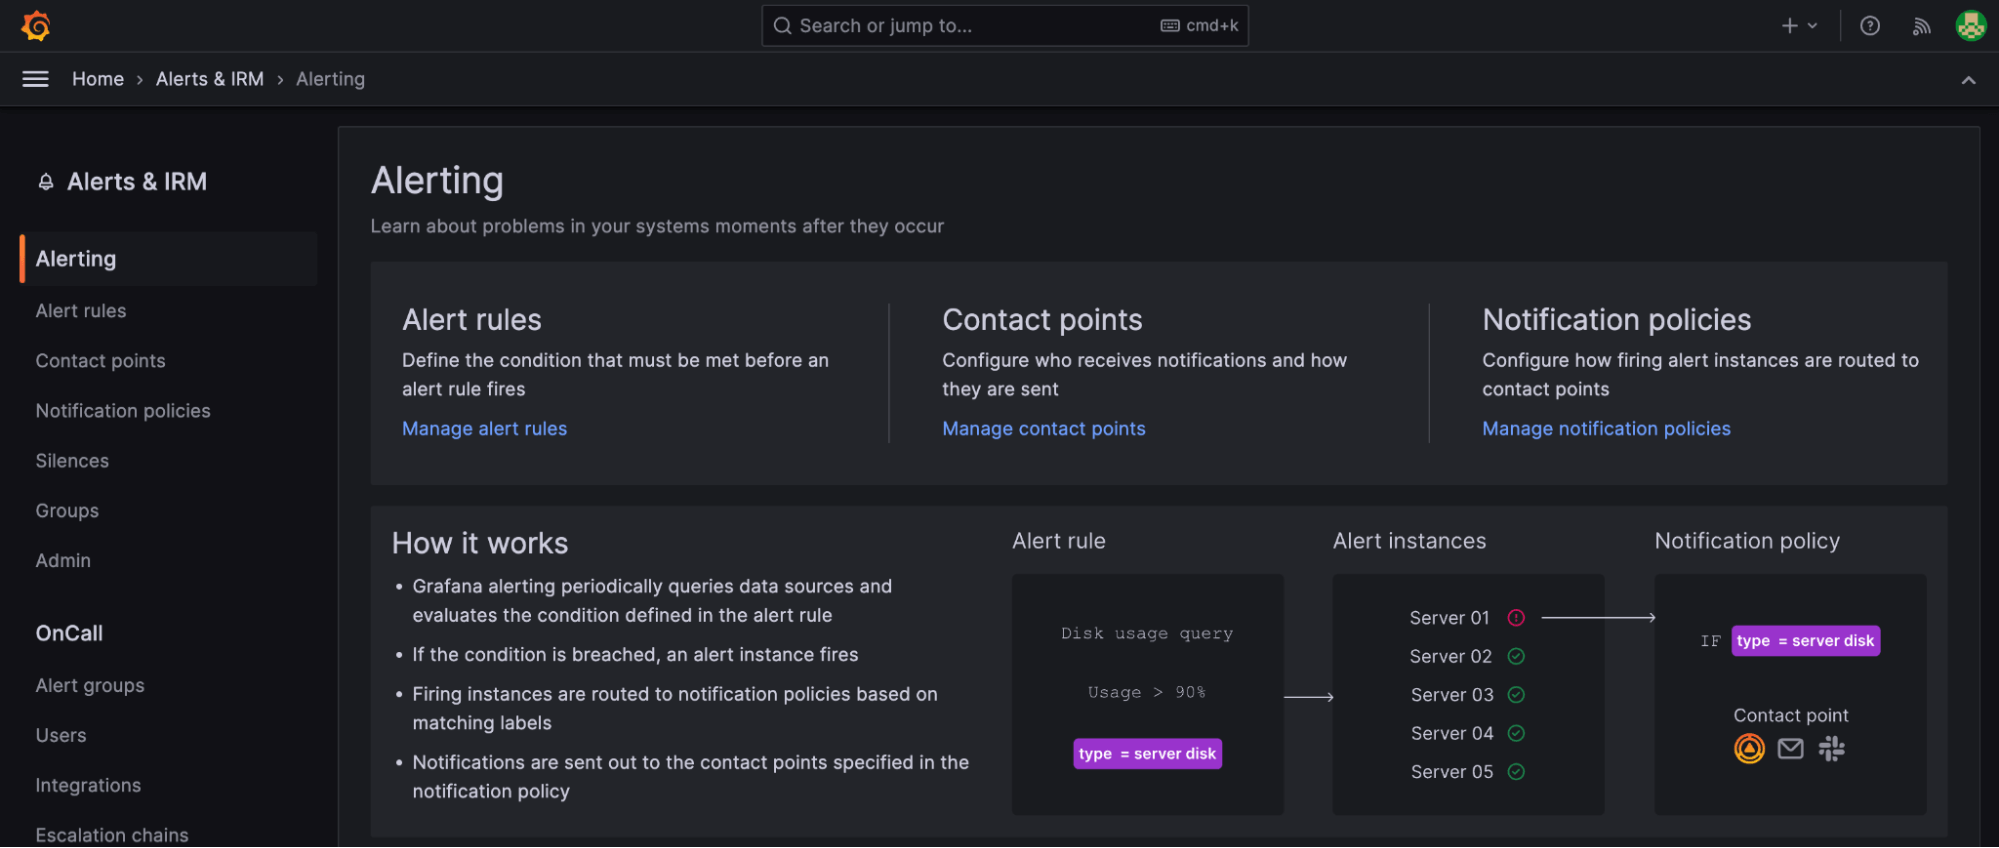
Grafana 9 introduced a unified alerting model that integrates with both legacy and new alert rules. To start, open the Grafana UI and navigate to Alerting > Alert rules. If you’re on an older version, switch to the Alerting tab in the left sidebar. The first step is to create a dashboard that visualises the metric you care about; alerts are tied to panels, not just raw queries.
1️⃣ Choose a data source that supports the query language you’ll use (Prometheus, InfluxDB, Elasticsearch, etc.). If you’re not sure, click the gear icon beside the data source name to view available features. Tip: Some data sources require you to enable remote write or metric ingestion for alerts to work properly.
2️⃣ Build a panel that displays the metric. Use the panel editor to add a query, apply transformations, and set a visual style. Once the panel renders the data you want, click Apply.
3️⃣ Configure alert rules directly in the panel editor. Click the Alert tab, then press Create alert rule. Define a name, set a frequency (how often Grafana evaluates the rule), and choose a condition such as “when the value is above 80%”. You can combine multiple conditions using logical operators.
4️⃣ Set alert evaluation logic. Grafana supports aggregation functions (avg, max, sum) and time windows. For example, “avg over last 5 minutes > 80%” catches sustained spikes rather than single outliers.
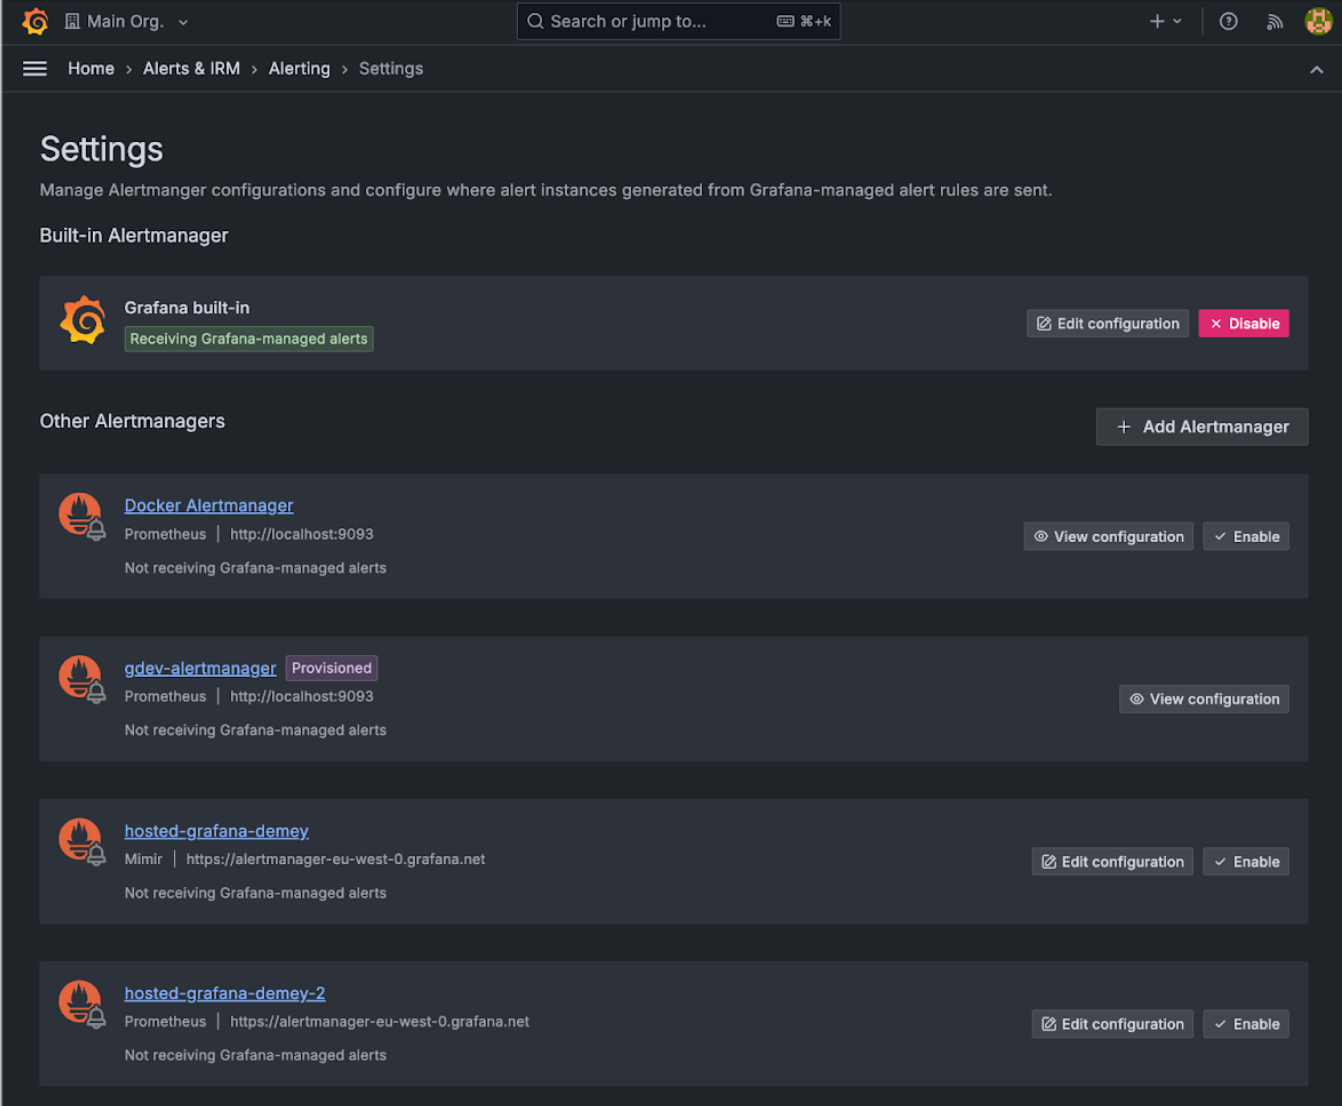
5️⃣ Define notifications. Under the Notifications section, add a channel (Slack, PagerDuty, Email, Webhook, etc.). Configure the channel’s URL, message format, and any additional parameters. Grafana’s notification system uses templates that can embed variables like ${ruleName} or ${value}, giving you context-rich alerts.
6️⃣ Save and test. After hitting Save, Grafana will automatically evaluate the rule and, if conditions are met, send a test notification to the configured channel. If you don’t receive a test alert, double‑check the channel settings and ensure that the data source is returning data.
Fine‑Tuning Alert Rules for Accuracy
Once you have a working alert, you’ll want to reduce noise and improve reliability. Below are common adjustments:
- Silencing periods – Schedule silences for known maintenance windows. Go to Alerting > Silences and set a start/end time.
- Suppression rules – Define conditions that suppress alerts when another higher‑priority alert fires.
- Deduplication – Group alerts by a key (e.g., instance name) to avoid duplicate notifications.
- Threshold hysteresis – Add a buffer (e.g., alert triggers above 80% but clears below 70%) to prevent flapping.
- Alert severity – Tag alerts with severity levels (critical, warning, info) and route them accordingly.
Testing edge cases is key. Simulate high load or downtime in a staging environment to ensure that the alert fires as expected. Grafana’s Alert History view shows a timeline of firing events, helping you diagnose false positives or missed triggers.
Integrating Grafana Alerts with Incident Management
Effective alerting is only the first part of incident management. Many teams use Grafana in combination with tools like PagerDuty, Opsgenie, or ServiceNow. To integrate:
- Webhooks – Grafana can send raw JSON payloads to any HTTP endpoint. Use these payloads to create incident tickets or trigger scripts.
- Grafana Cloud Alerts – If you’re on Grafana Cloud, you can push alerts directly to your cloud‑native incident platform.
- Custom integrations – Write a lightweight Lambda or Azure Function that listens to Grafana webhooks and pushes data into your internal monitoring system.
Always test the integration in a safe environment. Verify that the incident ticket contains the alert message, severity, and a direct link back to the Grafana dashboard.
Common Pitfalls and How to Avoid Them
Alerting can feel like a black art, but a few mistakes are surprisingly frequent:
- Using “when last” instead of “when avg over” – The former reacts to a single data point; the latter looks at trends, reducing false positives.
- Missing time zones – Grafana displays dashboards in UTC by default. If your data source timestamps in local time, set the timezone in the panel settings.
- Over‑aggregation – Aggregating too aggressively (e.g., summing across all nodes) can mask individual node failures. Use group by clauses wisely.
- Ignoring evaluation frequency – Setting a very low frequency (e.g., every 1 second) can overload your data source. A 1‑minute interval is often sufficient for most use cases.
Best Practices Checklist
- Document each alert’s purpose and owner.
- Use descriptive names like “DB‑Replica‑Lag‑Critical”.
- Keep alerting rules in source control (JSON export/import).
- Review alerts monthly to retire obsolete rules.
- Apply role‑based access control to limit who can edit alerts.
Frequently Asked Questions
- Can I use Grafana alerts with non‑Prometheus data sources? Yes. Most Grafana data sources now support alerting, but you should check the specific documentation for any quirks.
- What’s the difference between legacy and unified alerting? Legacy alerting is tied to individual dashboards and uses an older alerting syntax. Unified alerting is a centralized model introduced in Grafana 9, offering better rule management and richer notification options.
- How do I troubleshoot silent alerts? Verify the data source query returns data, check the evaluation frequency, and examine the alert history for any errors. Also, ensure your notification channels are correctly configured.