What You Need to Know About OSCPSE, OSS, and Hurricane Paths
When you hear the trio “OSCPSE, OSS, Hurricane Paths,” it can feel like a random mash‑up of tech jargon and weather talk. Yet each term sits at the crossroads of security, collaboration, and science—areas that increasingly overlap in today’s digital world. In this piece we’ll unpack what OSCPSE actually means, why open source software (OSS) matters more than ever, and how meteorologists chart hurricane tracks. By the end, you’ll have a clearer picture of these seemingly disparate topics and a few practical takeaways to apply.
What Is OSCPSE and Why It Matters to Security Professionals
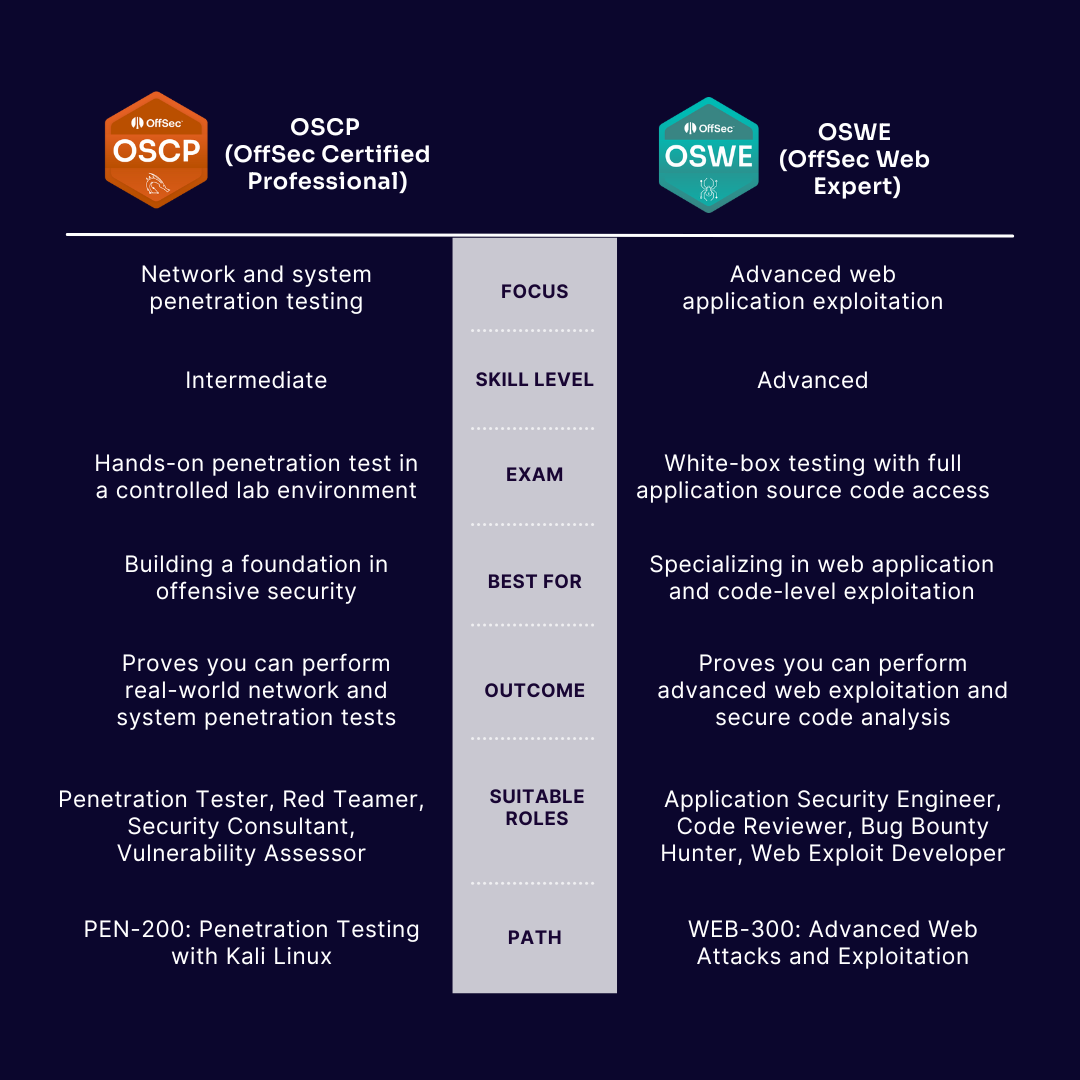
OSCPSE isn’t a brand you’ll find on a storefront; it’s a shorthand that surfaces in forums and study groups focused on the Offensive Security Certified Professional (OSCP) credential. In practice, OSCPSE usually refers to the “Offensive Security Certified Professional Study Environment”—the collection of labs, virtual machines, and tooling that candidates use to prepare for the exam.
The OSCP exam is famous for its hands‑on, “you‑must‑prove‑you‑can‑hack” approach. Rather than memorising theory, test‑takers must compromise a series of vulnerable machines within a limited time frame. That’s why the study environment matters: it mirrors the real‑world scenarios you’ll face, letting you experiment with tools like nmap, metasploit, and custom scripts without risking production systems.
Most candidates set up OSCPSE on a local hypervisor (VirtualBox or VMware) or rent a cloud‑based lab. The key is isolation—keeping your practice network separate from your home or work network to avoid accidental exposure. A well‑configured OSCPSE also includes snapshot capabilities, so you can roll back a machine after a failed exploit and try again without rebuilding the whole lab.
Beyond exam prep, the habits you develop in an OSCPSE—methodical enumeration, careful documentation, and a mindset of continual learning—translate directly to day‑to‑day penetration testing or red‑team work. In short, OSCPSE is less a product and more a disciplined workflow that underpins modern offensive security.
Understanding OSS: The Power of Open Source Software
Open source software (OSS) is software whose source code is publicly available for anyone to inspect, modify, and distribute. The OSS model emerged from collaborative projects like the Linux kernel and has since reshaped entire industries.
What sets OSS apart from proprietary alternatives? First, transparency. With the code open for review, security researchers can audit for vulnerabilities, and users can verify that there are no hidden backdoors. Second, community‑driven innovation. When a bug is discovered, developers worldwide can submit patches, often leading to faster fixes than in closed‑source products.
That collaborative spirit also fuels cost efficiency. Many organizations adopt OSS to avoid licensing fees, allocating budget instead to custom development or security hardening. However, “free” doesn’t mean “risk‑free.” Organizations need to manage supply‑chain risks, such as ensuring that third‑party libraries are up‑to‑date and sourced from reputable repositories.
Popular OSS projects—like the Apache web server, PostgreSQL database, and the Python programming language—illustrate how community stewardship can produce robust, enterprise‑grade tools. For security teams, integrating OSS means establishing clear policies for code review, patch management, and contribution guidelines.
How Hurricane Paths Are Tracked and Predicted
Predicting where a hurricane will travel combines physics, mathematics, and massive amounts of data. Meteorologists rely on numerical weather prediction (NWP) models that solve fluid‑dynamics equations governing the atmosphere. These models ingest satellite imagery, radar returns, buoy readings, and aircraft reconnaissance data.
One of the most widely used models is the Global Forecast System (GFS), which runs four times daily and projects conditions up to two weeks ahead. For tropical cyclones, specialized models like the Hurricane Weather Research and Forecasting (HWRF) model provide finer‑scale detail, focusing on the storm’s inner core, wind fields, and intensity.
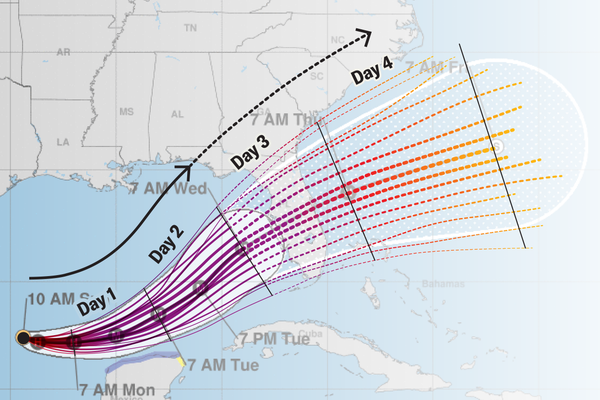
Once a model outputs a forecast track, forecasters overlay a “cone of uncertainty.” The cone widens with time because small errors in the initial data can amplify, a concept known as the butterfly effect. It’s why a hurricane’s exact landfall point remains probabilistic, even with sophisticated models.
Beyond models, human expertise remains vital. Meteorologists examine satellite loop movies, assess sea‑surface temperatures, and consider steering currents—large‑scale wind patterns that guide a storm’s movement. When these analyses align, agencies like the National Hurricane Center issue public advisories, watches, and warnings to keep communities informed.
Connecting the Dots: Security, Collaboration, and Forecasting
At first glance, OSCPSE, OSS, and hurricane paths seem unrelated, but they share a common thread: reliance on open data and collaborative processes. In OSCPSE, you simulate attacks on publicly documented vulnerabilities; in OSS, developers openly share code to improve security; and in hurricane forecasting, scientists share satellite data and model outputs to protect lives.
Understanding each domain can sharpen your overall analytical mindset. The disciplined, methodical approach you hone in an OSCPSE—documenting every step, verifying assumptions—mirrors how forecasters validate model outputs. Likewise, the OSS ethos of peer review encourages you to question and improve the tools you use for penetration testing.
If you’re a security professional, consider borrowing practices from the meteorological world: treat threat intelligence like weather data, continuously ingest new information, and update your defensive “forecast” accordingly. Conversely, if you’re a climate scientist, open‑source tools such as Python libraries for data analysis can accelerate research, much like they do in security testing.
Frequently Asked Questions
- What does OSCPSE stand for? It commonly refers to the “Offensive Security Certified Professional Study Environment,” a set of labs and tools used to prepare for the OSCP certification.
- How is open source software different from commercial software? OSS makes its source code freely available for inspection and modification, fostering transparency and community‑driven improvements, whereas commercial software typically restricts access to its code.
- Can I rely on hurricane track forecasts? Forecasts are probabilistic; the “cone of uncertainty” reflects possible paths. While models are highly advanced, it’s wise to follow official warnings and understand that exact landfall points can shift.
- Where can I practice OSCPSE safely? Many candidates use local virtualization platforms like VirtualBox or cloud labs offered by training providers. Ensure you isolate the lab network to prevent accidental exposure.